
Open source · Local policy enforcement
Give your agent tools.
Keep control of the calls.
Put a Cedar policy between your AI agent and its tools. Allow useful work, deny calls outside the rules, and keep signed decisions you can verify offline.
Your rules, in Cedar.
Start with a policy pack. Read and edit the rules before enabling enforcement.
A decision at the boundary.
Use an MCP wrapper or coding-agent hooks. Enforcement applies to calls routed through that setup.
A record you can keep.
Check signed decisions with the public key you trust, using the open verifier.
First run
Try it before connecting anything.
Use Node.js 22 and npm in a new directory. This creates a starter policy and a local signing key, then evaluates a proposed file read and force-push.
Expected: the read is allowed and the force-push is denied. Neither tool is executed. Evaluation stays local after installation.
Continue to signing and tamper detection ↗mkdir protect-mcp-demo
cd protect-mcp-demo
npm init -y
npm install --save-exact protect-mcp@0.32.3 @veritasacta/verify@0.11.0
npx --no-install protect-mcp init --starter
npx --no-install protect-mcp evaluate --policy ./protect.cedar --tool Read --input '{"path":"README.md"}'
npx --no-install protect-mcp evaluate --policy ./protect.cedar --tool Bash --input '{"command":"git push --force origin main"}' || test "$?" -eq 2Use it with your agent
Choose your connection.
Install policy hooks.
Preview the settings changes, install alongside existing hooks, then start the local policy server.
Open the setup guide ↗MCP serversWrap a tool server.
Start in shadow mode. Inspect calls and review the policy before switching to enforcement.
Open the wrapper guide ↗Other coding agentsCheck your host’s format.
Find the supported hook payloads and expected responses. Validate the connection in your own host.
See host integration notes ↗A gateway is one control in your setup. It covers routed calls; it is not an OS sandbox. A signature establishes signed bytes, not execution or a complete action history. Read the security boundary.
See the result
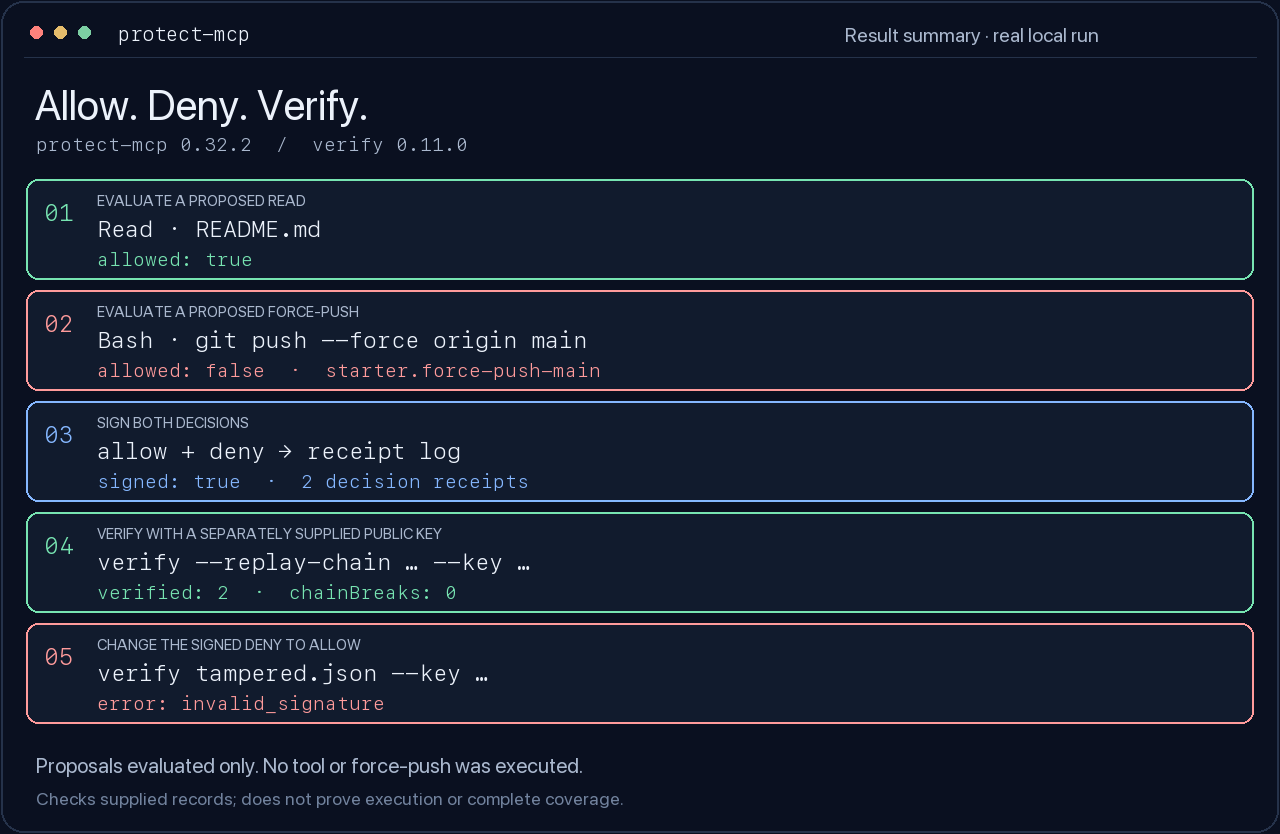
From a decision to a checkable receipt.
A summary of real CLI output from protect-mcp 0.32.2 and verifier 0.11.0. The source, captured outputs and regeneration scripts are public.
Text walkthrough and reproduction ↗
Open the full-size capture ↗
Public work
Contributions you can inspect.
Sources, integration versions and TRACE compatibility results. Contributions and integrations do not imply organizational endorsement.
Build with us
Make the next setup easier.
Test a host, contribute a useful policy fixture, or improve an installation guide. Each contribution should leave another developer with something they can reproduce.